Workspace API keys and MCP capabilities
Issue scoped keys for integrating systems.
Where to work
Issue scoped keys for integrating systems.
Step-by-step
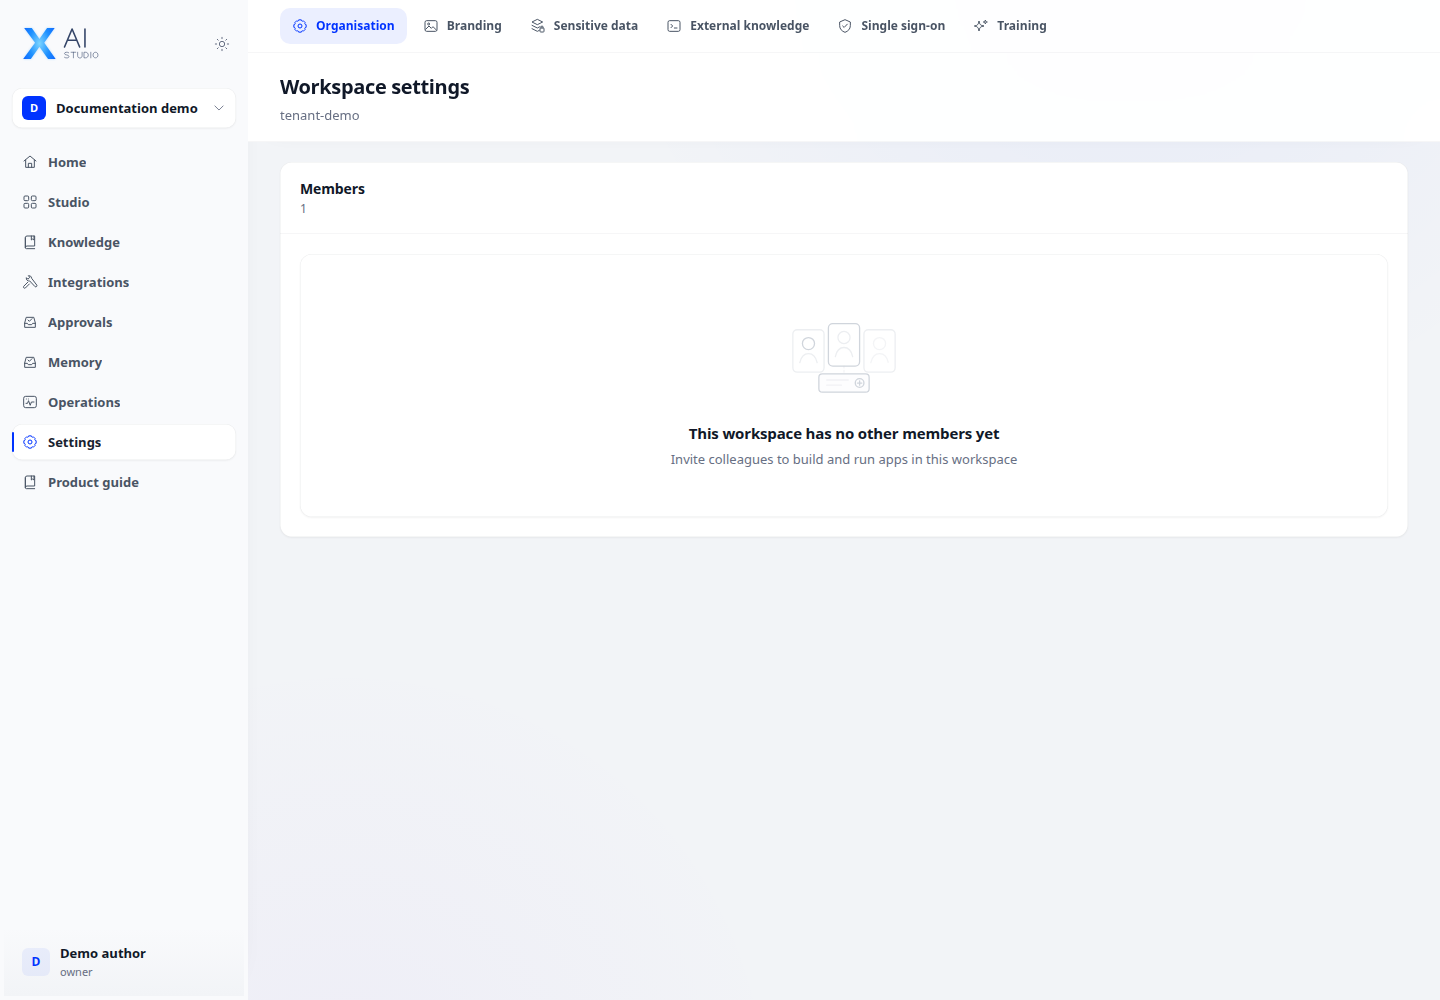
- Open workspace management → API keys, create a key and give it a recognisable name.
- Choose application scope and expiry. The default runs applications only; select mcp:author or mcp:admin only when needed.
- Save the key when first shown in your secret-management system, then test the integration with its granted scope.
- For workspace administration over MCP, use an app-unscoped key with mcp:admin and enable the MCP admin gate. Revoke unused keys.
Expected result
The key calls granted capabilities and stops working after expiry or revocation.
If it does not work
Declaring mcp:admin is insufficient while the admin gate is off. Some permissions, including others’ memories and provider credentials, never transfer over MCP.